EU GMP Annex 11: computerised systems that inspectors can trust
The 2011 Annex 11 still applies, and a much longer draft is waiting. Build to the current text and you will be most of the way to the draft.
In Short
- You stay responsible, even when a supplier hosts the system.
- Risk decides how much validation and which data controls you need.
- Audit trails are reviewed, not just switched on.
Electronic Records & Inspection Readiness Buyer Guide
For quality, regulatory, validation and IT teams evaluating electronic records, signatures and inspection readiness. Use it with or without V5.
- See what a signature must show.
- Check corrections keep the original.
- Know where Part 11 applies.
We ask for your name and email so we can handle this request. The full guide then opens on this site, ready to translate, print or save. Privacy policy. Practical orientation, not legal advice; your quality unit decides which rules apply.
 Ultimate
Free guide
Electronic Records & Inspection Readiness Buyer Guide
For quality, regulatory, validation and IT teams evaluating electronic records, signatures and inspection readiness. Use it with or without V5.
Annex 11 is part of EudraLex Volume 4, the EU guidelines for good manufacturing practice for medicinal products. It applies to computerised systems used in GMP activities. The version in force is dated 2011. On 7 July 2025 the European Commission and PIC/S published a full draft revision for consultation, with a new structure and much more detail on security, audit trails, identity management and cloud services. When we checked on 2 Oct 2026 the revised text had not been adopted, so this guide explains the current requirements and flags where the draft goes further. Annex 11 is a guideline that interprets the binding GMP rules; inspectors use it to judge GMP compliance.
Scope, risk and who is responsible
The 2011 text applies to all computerised systems used as part of GMP-regulated activities. Risk management should be applied throughout the lifecycle, and decisions on the extent of validation and data integrity controls should be based on a justified, documented risk assessment.
What applies now, and what is draft
- GuidanceEU GMP Annex 11 (2011)Current text
Computerised systems used in GMP. Inspectors use it to judge GMP compliance.
- GuidanceAnnex 11 draft revision (7 Jul 2025)Consultation draft, not adopted at 2 Oct 2026
Adds identity and access, security, alarms, cloud and audit trail detail.
- GuidanceChapter 4 draft and new Annex 22 (AI)Consultation drafts
Documentation and data integrity; artificial intelligence in GMP.
- Law21 CFR Part 11 (US)In force
Electronic records and signatures for FDA-regulated records.
More on scope, risk and who is responsible
The regulated user stays responsible even when a supplier or service provider builds or hosts the system: formal agreements should set out each party's responsibilities, and the competence and reliability of suppliers should be assessed. The draft keeps these ideas and adds detail on supplier oversight and cloud services.
Validation and Periodic Review
Clause 4 expects validation documentation covering the lifecycle, an up-to-date inventory of systems, user requirements traceable through the lifecycle, and evidence of appropriate test methods. Clause 11 expects periodic evaluation to confirm systems remain in a valid state.
More on validation and Periodic Review
The draft revision expands both, with more explicit expectations for requirements, testing and periodic review. Validation is done by the regulated company for its intended use; a supplier can provide documentation that supports it.
Data, audit trails and changes
Systems that exchange data electronically should include checks for correct and secure entry and processing. Data should be secured against damage, checked for accessibility and readability over the retention period, and backed up regularly.
Audit trail review: what to look for
Pick an entry to see why a reviewer would stop on it.
- Who changed it, why, and was the change approved?
More on data, audit trails and changes
Based on risk, systems should record GMP-relevant changes and deletions with a reason (an audit trail), and audit trails should be available, convertible to a generally intelligible form and regularly reviewed. The draft makes audit trail expectations more specific.
Electronic Signatures, Access and Security
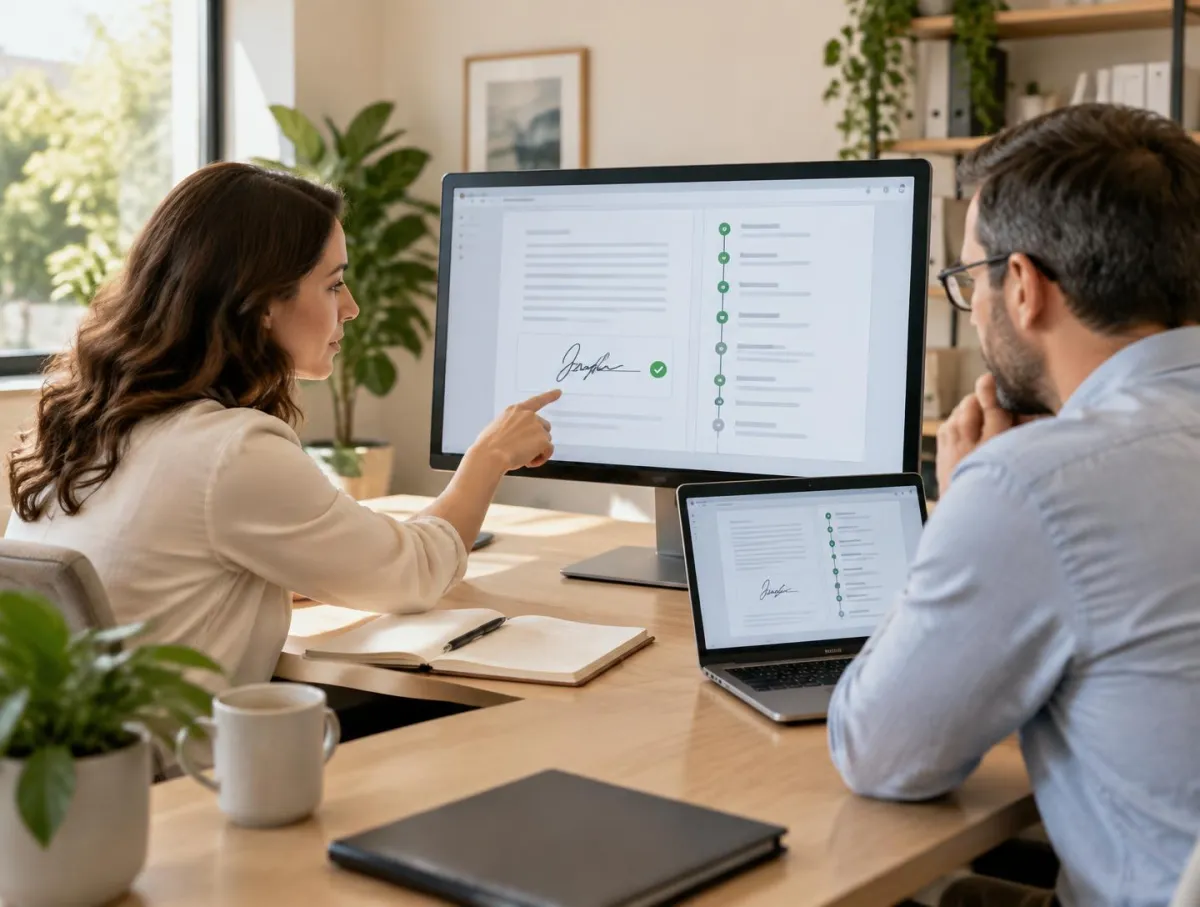
Electronic signatures should have the same impact as handwritten signatures within the company, be permanently linked to their record and include the time and date. Physical and logical controls should restrict access to authorised people.
More on electronic Signatures, Access and Security
The draft adds dedicated chapters on identity and access management and on security, treating cybersecurity as a GMP topic.
Incidents, Continuity and Archiving
All incidents, not only failures and data errors, should be reported and assessed, and the root cause of a critical incident identified as the basis for corrective and preventive action. There should be provisions for continuity of processes that depend on computerised systems if they break down, and archived data should be checked for accessibility, readability and integrity.
More on incidents, Continuity and Archiving
The draft keeps backup and archiving as separate chapters.
Questions
Is the revised Annex 11 in force?
Not when we checked on 2 Oct 2026. The European Commission and PIC/S published the draft on 7 July 2025 for consultation. The 2011 version remains the current text until a revised version is adopted and its effective date is published. Check the EudraLex Volume 4 page for the current status.
How is Annex 11 different from 21 CFR Part 11?
Part 11 is a US regulation focused on electronic records and electronic signatures. Annex 11 is an EU GMP guideline covering the whole lifecycle of computerised systems used in GMP, including risk management, suppliers, validation, incidents and continuity. Companies selling into both markets usually design one approach that meets both.
Does a cloud or SaaS supplier make us compliant?
No. The regulated company stays responsible. Annex 11 expects formal agreements setting out responsibilities, assessment of the supplier, and validation for your intended use. A supplier's documentation and quality system can support that work.
Which other EU documents were revised alongside Annex 11?
In July 2025 the Commission also consulted on a revised Chapter 4 (Documentation) and a new Annex 22 on artificial intelligence. Check EudraLex Volume 4 for the status of each.
Practical orientation, not legal advice. Rules differ by jurisdiction; your quality and compliance team decides what applies.
Keep reading
 EU GMP Annex 1 Guide: Contamination Control Strategy, APS and PUPSIT
 EU GMP for Medicinal Cannabis: GACP, Annex 7 and Herbal Starting Materials
 EU GMP Guide: EudraLex Volume 4 Chapters, Annexes and Who Decides
- 21 CFR Part 11 Readiness Guide for Regulated Manufacturers
 EU Acrylamide Regulation 2017/2158: Mitigation, Sampling and Benchmark Levels
 AI and 21 CFR Part 11: Where AI Fits in Regulated Records